Three Chained Zero-Days Defeat Windows Browser Sandboxes in AI-Driven Research
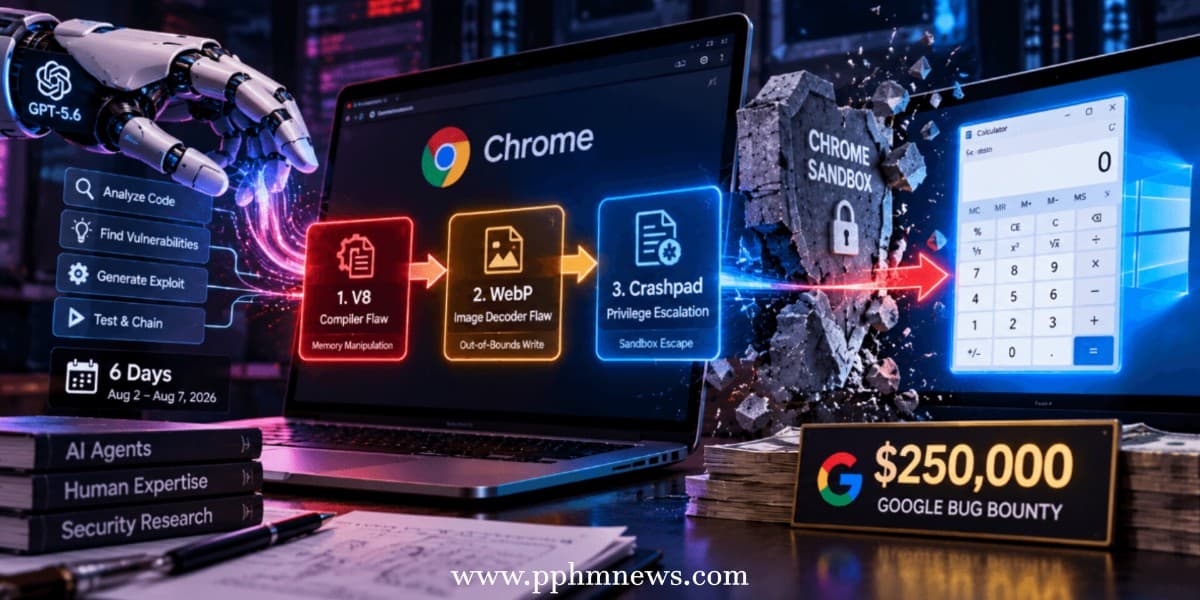
Security firm XBOW has received a $250,000 vulnerability reward from Google after demonstrating a sophisticated attack chain that escaped Chrome's security sandboxes and executed code on Windows.
The research, disclosed October 13, 2026, combined three previously unknown vulnerabilities into a working exploit triggered by loading a specially crafted webpage.
XBOW developed the awarded chain between August 2 and August 7 using human-directed AI agents powered by OpenAI's GPT-5.6 Sol model.
Google has confirmed and patched all three vulnerabilities. There is no reported evidence that the chain was exploited against Chrome users.
Six-Day Research Campaign Breaks Browser Isolation
XBOW researcher Brendan Dolan-Gavitt collaborated with Andres Luksenberg, Baul Lee, and Willem Pinckaers to investigate Chrome's security architecture.
Human Expertise Guides Automated Discovery
AI agents examined source code, tested hypotheses, developed proofs of concept, and helped integrate individual exploitation stages.
Researchers selected targets, evaluated findings, and redirected unsuccessful investigations.
XBOW estimated approximately $40,000 in API expenses during the six-day effort, excluding personnel costs and earlier research.
The team demonstrated successful exploitation by launching Windows Calculator from a webpage opened in a signed Chrome Beta build.
Three Vulnerabilities Enable Complete Sandbox Escape
The attack exploited weaknesses across Chrome's JavaScript engine, image decoder, and crash-reporting infrastructure.
V8 Compiler Error Enables Memory Manipulation
The first vulnerability affected Maglev, V8's optimizing JavaScript compiler.
During deoptimization, the compiler incorrectly reused a mutableHeapNumber, creating inconsistent assumptions about object values.
Researchers exploited this behavior to obtain read-and-write access within V8's four-gigabyte pointer-compression region.
WebP Processing Flaw Crosses the First Boundary
The second vulnerability, CVE-2026-85045, affected animated WebP processing through the WebCodecsImageDecoderinterface.
A timing inconsistency between cached image dimensions and modified image data caused an out-of-bounds write.
This enabled manipulation of native renderer memory and execution outside V8's sandbox.
Crash Reporting Weakness Completes the Compromise
The final stage targeted Crashpad, Chrome's crash-reporting component, which operates outside the renderer sandbox.
Memory Corruption Reaches a Privileged Process
Researchers exploited a Windows thread-handling race condition that allowed memory protections to change while Crashpad assumed the target process was suspended.
An oversized memory-read retry subsequently overflowed a buffer and corrupted an adjacent object.
By redirecting existing handler functionality, the researchers launched Windows Calculator outside the renderer's containment boundary.
Findings Highlight Faster Exploit Development
Google addressed the vulnerabilities by correcting mutable-number handling, enforcing image-buffer boundaries, and restricting Crashpad retry lengths.
Defensive Research Gains Speed, but Expertise Remains Essential
The $250,000 payment represents the first full-chain award under Google's 2026 Chrome reward framework.
The demonstration illustrates how AI can accelerate complex vulnerability research, although the six-day timeline benefited from previous experiments, established tooling, and substantial human expertise.
Organizations should ensure Chrome is updated and relaunched to activate installed security fixes.
The broader security implication is that sophisticated exploit chains may become faster to develop, increasing the importance of rapid patch deployment and continuous vulnerability research.