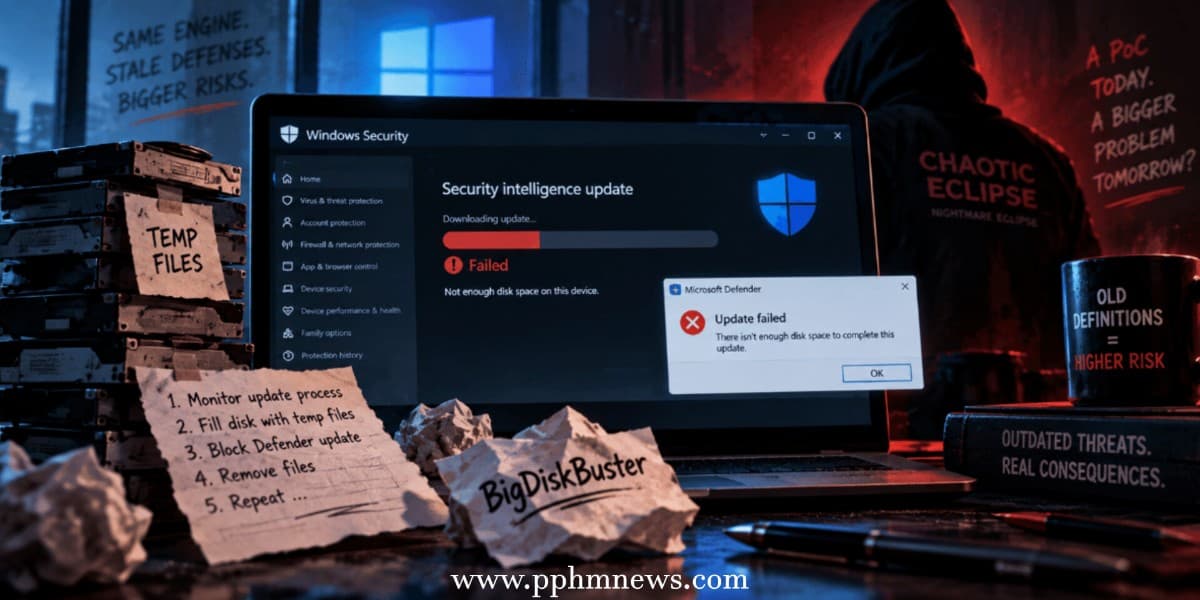
BigDiskBuster Targets Defender’s Update Pipeline Through Disk Exhaustion
Security researcher Abdelhamid Naceri, also known as Nightmare Eclipse and Chaotic Eclipse, has released a proof-of-concept tool designed to prevent Microsoft Defender Antivirus from installing platform and security-intelligence updates.
Dubbed BigDiskBuster, the technique does not shut down Defender or directly disable real-time protection. Instead, it interferes with the update process, potentially leaving an otherwise active antivirus installation dependent on outdated components and malware definitions.
The researcher claims the technique works across all currently supported Windows versions, although that assertion has not been independently verified.
Disk Space Becomes the Attack Vector
BigDiskBuster monitors activity associated with Defender's update process. When an update begins, the PoC attempts to consume the remaining free space on the Windows system drive using hidden temporary files.
Because Defender requires available storage to stage and install updates, exhausting that capacity can cause the update operation to fail.
Once the attempted update ends, the temporary files can be removed and the occupied storage returned—allowing the tool to repeat the interference when another update starts.
MRT.exe Is Targeted Separately
The PoC also opens Microsoft's Malicious Software Removal Tool (MRT.exe) with restrictive sharing permissions.
Holding the file in this state can interfere with other processes attempting to modify or replace it. However, available evidence does not establish how significant this behavior is to the Defender update failure itself.
Defender Can Remain Active but Fall Behind
The security implication is more subtle than simply crashing antivirus software.
If an attacker can continuously prevent security-intelligence updates, Defender may remain operational while gradually losing visibility into newly identified malware. That creates a potential window in which endpoint protection appears functional but lacks the latest detection content.
Naceri described BigDiskBuster as similar to his earlier UnDefend research and acknowledged that the current implementation remains buggy and requires additional work.
No Confirmed Exploitation or Microsoft Fix Yet
As of publication, there is no public evidence that BigDiskBuster has been deployed in real-world attacks, and Microsoft's public vulnerability records do not yet provide a CVE or dedicated security advisory for the reported issue.
Microsoft had also not publicly confirmed the researcher's broad affected-version claim in the reporting reviewed for this article.
For defenders, repeated antivirus-update failures deserve investigation, particularly when accompanied by unexplained temporary disk exhaustion.
BigDiskBuster highlights an important endpoint-security principle: protecting an antivirus engine is not sufficient if an attacker can reliably prevent that engine from receiving the intelligence it needs to recognize emerging threats.