Stolen Login Details Enable Months of Unauthorized Activity Inside Banking Infrastructure
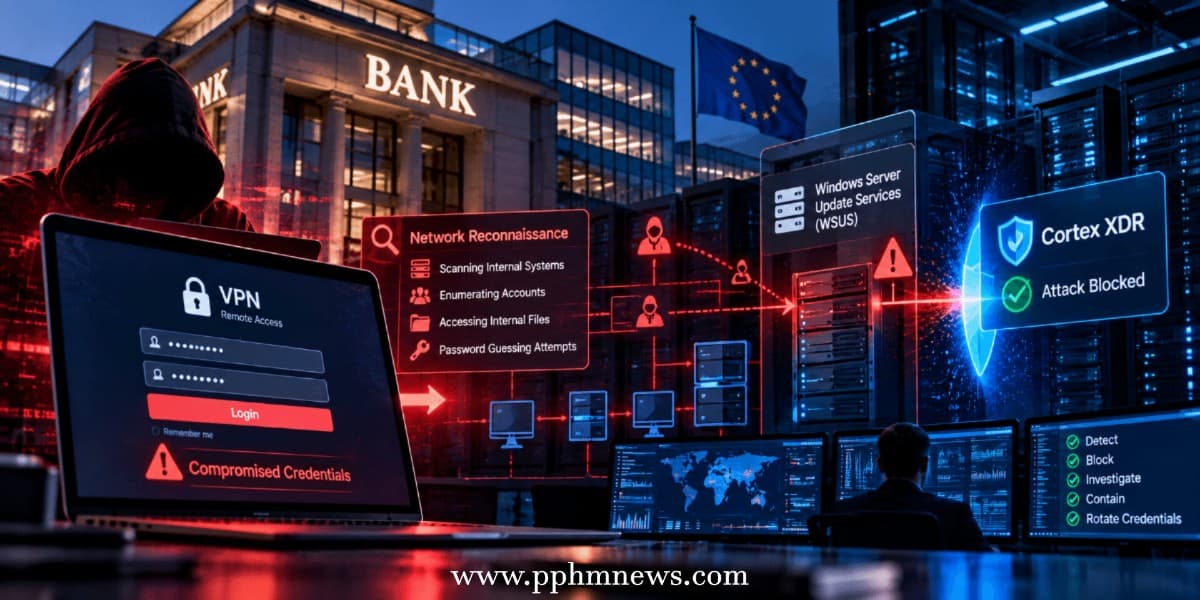
A European bank suffered a prolonged cybersecurity intrusion after an attacker used compromised credentials to access its internal network through an improperly configured, third-party-managed remote access gateway.
The incident, investigated by Palo Alto Networks Unit 42, involved extensive network reconnaissance, repeated password-guessing attempts, and an attempted compromise of a critical Windows management server.
Endpoint security controls ultimately blocked the attacker's escalation attempt. Investigators reported finding no additional persistent access mechanisms.
The bank's identity and the origin of the stolen credentials have not been disclosed.
Third-Party Gateway Becomes Initial Entry Point
The attacker entered through an externally accessible VPN appliance whose authentication configuration failed to adequately restrict access.
Valid Accounts Bypass Perimeter Defenses
Rather than exploiting a previously unknown software vulnerability, the intruder authenticated using legitimate but compromised credentials.
Once connected, the attacker gained access to internal resources and began examining the bank's network architecture.
The incident highlights the risks associated with outsourced infrastructure when authentication policies and access privileges are not consistently enforced.
Extensive Reconnaissance Exposes Internal Resources
The intruder conducted repeated scans across thousands of internal systems, searching for accessible services and opportunities to expand access.
Administrator Accounts Face Repeated Attacks
Over several months, the attacker launched password-guessing campaigns targeting internal accounts, particularly those with administrative privileges.
The activity also included systematic browsing of internal documentation and shared storage locations.
Automated requests retrieved webpages and attachments, potentially exposing operational details useful for subsequent attacks.
However, the investigation did not establish the volume of information removed or confirm a broader data-exfiltration operation.
Windows Management Server Becomes Escalation Target
The attacker eventually attempted to exploit a remote code execution weakness in Windows Server Update Services (WSUS) on a central configuration management server.
Endpoint Detection Interrupts the Attack
Compromising the server could have provided access to software deployment functions and opportunities for broader network control.
According to the incident report, Cortex XDR detected the unauthorized execution attempt and prevented the attacker from successfully escalating access.
The published account does not identify the specific WSUS vulnerability or establish which exploit technique was used.
Investigation Finds No Additional Persistence
Following detection, Unit 42 examined endpoint telemetry across thousands of devices and reviewed logs from dozens of Windows and Linux servers.
Credential Rotation Supports Containment
Investigators reported no evidence of additional attacker footholds or persistent backdoors.
The bank subsequently rotated compromised credentials, reviewed exposed internal documentation, and expanded its security monitoring capabilities.
These measures addressed both the immediate intrusion and weaknesses that could have enabled renewed access.
Identity Security Remains a Critical Banking Defense
The case demonstrates how attackers can exploit legitimate authentication mechanisms without relying on sophisticated malware.
Stronger Controls Limit Lateral Movement
Financial institutions should enforce phishing-resistant multifactor authentication, restrict privileged accounts, continuously audit third-party access, and monitor unusual authentication patterns.
Network segmentation and timely patching of management infrastructure can further reduce the consequences of compromised credentials.
The central lesson is that a valid login should never automatically translate into unrestricted network trust, particularly when remote access infrastructure is managed by external providers.